
A recent variant of the Mirai malware has been observed targeting 13 IoT vulnerabilities to ensnare devices into a botnet.
The post Mirai Variant V3G4 Targets 13 Vulnerabilities to Infect IoT Devices appeared first on SecurityWeek.




A recent variant of the Mirai malware has been observed targeting 13 IoT vulnerabilities to ensnare devices into a botnet.
The post Mirai Variant V3G4 Targets 13 Vulnerabilities to Infect IoT Devices appeared first on SecurityWeek.

The National Institute of Standards and Technology (NIST) has selected a group of cryptographic algorithms called Ascon as the lightweight cryptography standard to protect data flowing through IoT devices.
Following a multi-year effort that included security code reviews, NIST announced the Ascon family of algorithms will soon be the standard to protect data created and transmitted by the Internet of Things (IoT), including its myriad tiny sensors and actuators.
The Ascon algorithms, developed in 2014 by a team of cryptographers from Graz University of Technology, Infineon Technologies, Lamarr Security Research and Radboud University, are designed for miniature technologies such as implanted medical devices, stress detectors inside roads and bridges, and keyless entry fobs for vehicles.
According to NIST, these tiny devices need “lightweight cryptography” — protection that uses the limited amount of electronic resources they possess
The Ascon family was selected in 2019 as the primary choice for lightweight authenticated encryption in the final portfolio of the CAESAR competition, a sign that Ascon had withstood years of examination by cryptographers, NIST said in a note announcing the choice.
“The world is moving toward using small devices for lots of tasks ranging from sensing to identification to machine control, and because these small devices have limited resources, they need security that has a compact implementation,” said NIST computer scientist Kerry McKay. “These algorithms should cover most devices that have these sorts of resource constraints.”
The standards body expects Ascon to power two of the most important tasks in lightweight cryptography: authenticated encryption with associated data (AEAD) and hashing.
The Institute made it clear that the new algorithms are not intended to be used for post-quantum encryption.
“One of the Ascon variants offers a measure of resistance to the sort of attack a powerful quantum computer might mount. However, that’s not the main goal here,” McKay said. “Post-quantum encryption is primarily important for long-term secrets that need to be protected for years. Generally, lightweight cryptography is important for more ephemeral secrets.”
Related: Is OTP a Viable Alternative to NIST’s Post-Quantum Algorithms?
Related: CISA: Critical Infrastructure Must Prep for Post-Quantum Cryptography
Related: NIST Post-Quantum Algorithm Finalist Cracked Using a Classical PC
Related: NIST Announces Post Quantum Encryption Competition Winners
The post NIST Picks Ascon Algorithms to Protect Data on IoT, Small Electronic Devices appeared first on SecurityWeek.

Australia’s Defense Department will remove surveillance cameras made by Chinese Communist Party-linked companies from its buildings, the government said Thursday after the U.S. and Britain made similar moves.
The Australian newspaper reported Thursday that at least 913 cameras, intercoms, electronic entry systems and video recorders developed and manufactured by Chinese companies Hikvision and Dahua are in Australian government and agency offices, including the Defense Department and the Department of Foreign Affairs and Trade.
Hikvision and Dahua are partly owned by China’s Communist Party-ruled government.
Australian Defense Minister Richard Marles said his department is assessing all its surveillance technology.
“Where those particular cameras are found, they’re going to be removed,” Marles told Australian Broadcasting Corp. “There is an issue here and we’re going to deal with it.”
Asked about Australia’s decision, Chinese Foreign Ministry spokesperson Mao Ning criticized what she called “wrongful practices that overstretch the concept of national security and abuse state power to suppress and discriminate against Chinese enterprises.”
Without mentioning Australia by name, Mao said the Chinese government has “always encouraged Chinese enterprises to carry out foreign investment and cooperation in accordance with market principles and international rules, and on the basis of compliance with local laws.”
“We hope Australia will provide a fair and non-discriminatory environment for the normal operation of Chinese enterprises and do more things that are conducive to mutual trust and cooperation between the two sides,” she told reporters at a daily briefing.
The U.S. government said in November it was banning telecommunications and video surveillance equipment from several prominent Chinese brands including Hikvision and Dahua in an effort to protect the nation’s communications network.
Security cameras made by Hikvision were also banned from British government buildings in November.
An audit in Australia found that Hikvision and Dahua cameras and security equipment were found in almost every department except the Agriculture Department and the Department of Prime Minister and Cabinet.
The Australian War Memorial and National Disability Insurance Agency have said they will remove the Chinese cameras found at their sites, the ABC reported.
Opposition cybersecurity spokesman James Paterson said he had prompted the audit by asking questions over six months of each federal agency, after the Home Affairs Department was unable to say how many of the cameras, access control systems and intercoms were installed in government buildings.
“We urgently need a plan from the … government to rip every one of these devices out of Australian government departments and agencies,” Paterson said.
Both companies are subject to China’s National Intelligence Law which requires them to cooperate with Chinese intelligence agencies, he said.
“We would have no way of knowing if the sensitive information, images and audio collected by these devices are secretly being sent back to China against the interests of Australian citizens,” Paterson said.
Related: US Says Chinese Military Behind Vast Aerial Spy Program
The post Australian Defense Department to Remove Chinese-Made Cameras appeared first on SecurityWeek.

Researchers have discovered a vulnerability that can be exploited by remote hackers to tamper with the timestamp of videos recorded by Dahua security cameras.
The flaw, tracked as CVE-2022-30564, was discovered last year by India-based CCTV and IoT cybersecurity company Redinent Innovations. Advisories describing the vulnerability were published on Wednesday by both Dahua and Redinent.
Redinent has assigned the vulnerability a ‘high’ severity rating, but Dahua has calculated a 5.3 CVSS score for it, which makes it ‘medium severity’.
According to the Chinese video surveillance equipment maker, the flaw impacts several types of widely used cameras and video recorders, including IPC, SD, NVR, and XVR products.
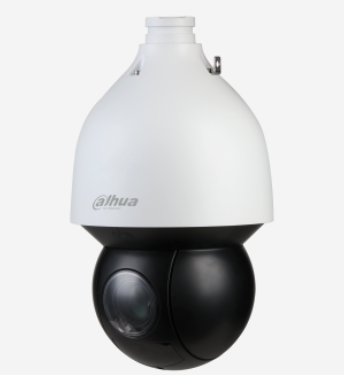
An attacker can exploit the vulnerability to modify a device’s system time by sending it a specially crafted packet.
Redinent says there are thousands of internet-exposed cameras that can be targeted directly by hackers. Exploitation from the local network is also possible. However, the company noted that an attacker needs to have knowledge of an APIs parameters in order to exploit the vulnerability.
“An attacker can make modification to the timestamp of the video feed, leading to inconsistent date and time showing up on the recorded video, without the need of knowing the username and password of the camera. It has a direct impact on digital forensics,” Redinent explained in its advisory.
Dahua device vulnerabilities may be targeted by DDoS botnets, but in the case of CVE-2022-30564, it would most likely be exploited in highly targeted attacks whose goal is to tamper with evidence, rather than cybercrime operations.
The issue was reported to the vendor in the fall of 2022. Dahua has released patches for each of the impacted devices.
In December, Redinent disclosed a vulnerability affecting Hikvision wireless bridges. Exploitation of the flaw could lead to remote CCTV hacking.
Related: Backdoor Found in Dahua Video Recorders, Cameras
Related: CISA Warns of Hikvision Camera Flaw as U.S. Aims to Rid Chinese Gear From Networks
Related: FCC: Telecom Firms Requested $5.6 Billion to Replace Chinese Gear
The post Vulnerability Allows Hackers to Remotely Tamper With Dahua Security Cameras appeared first on SecurityWeek.

Researchers warn that many electric vehicle (EV) charging management systems are affected by vulnerabilities that could allow hackers to cause disruption, steal energy, or obtain driver information.
The vulnerabilities were discovered by researchers working for SaiFlow, an Israel-based company that specializes in protecting EV charging infrastructure and distributed energy resources.
The security holes are related to the communications between the charging system management service (CSMS) and the EV charge point (CP), specifically the use of the Open Charge Port Protocol (OCPP). The flaws have been confirmed to impact the CSMS offered by multiple vendors.
The problem is related to the use of WebSocket communications by the OCPP and how it mishandles multiple connections. The protocol does not know how to handle more than one CP connection at a time and attackers could abuse this by opening a new connection to the CSMS. Another issue is related to what SaiFlow describes as “weak OCPP authentication and chargers identities policy”.
By opening a new connection to the CSMS on behalf of a charge point, the attacker causes the original connection to be closed or to become nonfunctional.
According to SaiFlow, an attacker can exploit the weaknesses to launch a distributed denial-of-service (DDoS) attack that disrupts the electric vehicle supply equipment (EVSE) network. In addition, if an attacker can connect to the CSMS, they may be able to obtain drivers’ personal information, including payment card data, as well as other sensitive data, such as server credentials.
In certain configurations, if the charger approves unknown driver identities, an attacker may be able to charge their vehicle without paying for it, the security firm said.
“Since the CSMS platforms are publicly accessible, it is possible for an attacker to hijack the connection remotely, without needing to gain credentials, access, or perform MITM attacks,” Ron Tiberg-Shachar, co-founder and CEO of SaiFlow, told SecurityWeek.
Tiberg-Shachar believes it may be possible for a somewhat inexperienced hacker to carry out an attack, even with limited resources.
In order to conduct an attack, the hacker first needs to obtain a charger’s identity. This identity typically has a standard structure, making it easier for threat actors to enumerate the values of valid identifiers.
In the next phase, they need to obtain information on which CSMS platform the charger is connected to. The expert noted that the CSMS URL can be discovered using services such as Shodan or SecurityTrails.
SaiFlow has published a technical blog post describing the vulnerabilities and the attack scenarios. The company also provides recommendations for how these types of attacks can be mitigated.
It doesn’t seem like the vulnerabilities can be easily patched by vendors.
“We’ve approached many key players in the industry (and keep on doing so) to make them aware of our findings and how they can approach a solution,” Tiberg-Shachar said. “Additionally, we’ve made our solutions team available to support any specific technical questions, in an effort to reinforce vulnerabilities as quickly as possible. Our key goal is to support partners in scaling their charging infrastructure as quickly and safely as possible.”
Related: Unpatched Econolite Traffic Controller Vulnerabilities Allow Remote Hacking
Related: Remote ‘Brokenwire’ Hack Prevents Charging of Electric Vehicles
Related: New Flaws Expose EVlink Electric Vehicle Charging Stations to Remote Hacking
The post EV Charging Management System Vulnerabilities Allow Disruption, Energy Theft appeared first on SecurityWeek.

Attack surface management firm Censys has identified roughly 30,000 internet-exposed QNAP network-attached storage (NAS) appliances that are likely affected by a recently disclosed critical-severity code injection vulnerability.
Tracked as CVE-2022-27596 (CVSS score of 9.8), the security defect is described as an SQL injection bug that allows remote attackers to inject malicious code into vulnerable NAS devices.
The issue impacts all devices that run QTS 5.0.1 and QuTS hero h5.0.1, and Censys says that nearly 30,000 devices running a vulnerable software version can be found on the internet.
However, the number of affected devices could be much higher, the company warns. Censys has identified over 67,000 hosts that run QNAP software, but it could not retrieve the version information for 37,000 of them.
Most of the identified vulnerable hosts are in Italy (3,200) and the US (3,149). Taiwan (1,942), Germany (1,881), and Japan (1,714) round up the top five list.
“If the exploit is published and weaponized, it could spell trouble to thousands of QNAP users. Everyone must upgrade their QNAP devices immediately to be safe from future ransomware campaigns,” Censys notes.
QNAP appliances are known to be a target for cybercriminals, and the recent Deadbolt ransomware attacks are proof of that. At its peak, the threat had infected over 20,000 devices, allowing cybercriminals to steal roughly $200,000 from victims.
“While there are no indications that bad actors are using this new exploit, the threat is definitely on the horizon,” Censys underlines.
QNAP has patched the vulnerability with the release of QTS 5.0.1.2234 build 20221201 and QuTS hero h5.0.1.2248 build 20221215. Users are advised to update their devices as soon as possible and to make sure that they are not accessible directly from the internet.
Related: QNAP Patches Critical Vulnerability in Network Surveillance Products
Related: QNAP Warns NAS Users of DeadBolt Ransomware Attacks
Related: ‘Raspberry Robin’ Windows Worm Abuses QNAP Devices
The post 30k Internet-Exposed QNAP NAS Devices Affected by Recent Vulnerability appeared first on SecurityWeek.

Printer and imaging products manufacturer Lexmark this week published a security advisory to warn users of a critical vulnerability impacting over 120 printer models.
The issue, tracked as CVE-2023-23560 (CVSS score of 9.0), is described as a server-side request forgery (SSRF) flaw in the Web Services feature of newer Lexmark devices, which could be exploited to execute arbitrary code.
“Successful exploitation of this vulnerability can lead to an attacker being able to remotely execute arbitrary code on a device,” Lexmark warns in an advisory (PDF).
The manufacturer lists roughly 125 device models that are impacted by the security defect, including B, C, CS, CX, M, MB, MC, MS, MX, XC, and XM series printers.
The company has announced firmware updates that resolve the vulnerability on all impacted devices and encourages users to find update instructions on its support website.
Additionally, Lexmark says that exploitation of CVE-2023-23560 can be blocked by disabling the Web Services feature on the vulnerable printers (TCP port 65002).
To block TCP port 65002, users would have to go to Settings > Network/Ports > TCP/IP > TCP/IP Port Access, uncheck TCP 65002 ( WSD Print Service ), and then click Save.
Lexmark also warns that, while it is not aware of any malicious attacks targeting the vulnerability, proof-of-concept (PoC) code exploiting it has been made public.
Given that it is not unusual for threat actors to target unpatched printers and other Internet of Things (IoT) devices, users are advised to apply the available patches as soon as possible.
Related: Hundreds of Thousands of Konica Printers Vulnerable to Hacking via Physical Access
Related: Serious Vulnerability Exploited at Hacking Contest Impacts Over 200 HP Printers
Related: Xerox Quietly Patched Device-Bricking Flaw Affecting Some Printers
The post Critical Vulnerability Impacts Over 120 Lexmark Printers appeared first on SecurityWeek.

Vulnerabilities identified in TP-Link and NetComm router models could be exploited to achieve remote code execution (RCE).
Two security defects were identified in TP-Link WR710N-V1-151022 and Archer-C5-V2-160201 SOHO (small office/home office) routers, allowing attackers to execute code, crash devices, or guess login credentials.

The US Department of Defense (DoD) is getting ready to launch the third installment of its ‘Hack the Pentagon’ bug bounty program, which will focus on the Facility Related Controls System (FRCS) network.

A hacktivist group has made bold claims regarding an attack on an industrial control system (ICS) device, but industry professionals have questioned their claims.
Impostazioni privacy
Questo sito utilizza i cookie per migliorare la tua esperienza di navigazione su questo sito.
