A prominent security researcher poking around at the Zoom video conferencing platform found worrying signs the company failed to enable a decades-old anti-exploit mitigation, a blunder that greatly increased exposure to malicious hacker attacks.




A prominent security researcher poking around at the Zoom video conferencing platform found worrying signs the company failed to enable a decades-old anti-exploit mitigation, a blunder that greatly increased exposure to malicious hacker attacks.

Thousands of industrial organizations worldwide have been hit in campaigns that leverage short-lived malware to harvest corporate credentials that are then sold by threat actors for a profit, according to Kaspersky.


A vulnerability in Box’s implementation of multi-factor authentication (MFA) allowed attackers to take over victim’s accounts without having access to the victim’s phone, according to new research from Varonis.

The sudden move by Russia’s top law enforcement agency to conduct a very public takedown of the REvil ransomware operation has set tongues wagging about how diplomacy may hold the key to slowing big-game ransomware attacks.

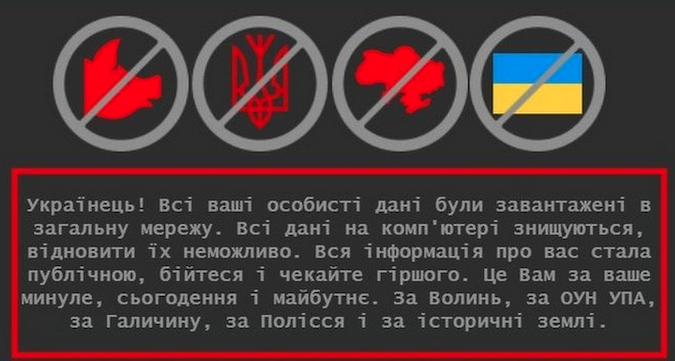
Newly detected WhisperGate malware being used by previously unknown threat group in cyberattacks against Ukraine

Researchers at cloud security startup Orca Security have publicly documented a pair of vulnerabilities in AWS CloudFormation and AWS Glue that attackers could use to leak sensitive files or access other customers’ data.

Russia on Friday said it has cracked down on the infamous REvil hacking group, known for its high profile supply chain attack against software maker Kaseya, and a ransomware attack against JBS USA that forced the shutdown of a portion of the world’s largest meat processing company.

Federal Communications Commission (FCC) chairwoman Jessica Rosenworcel this week proposed updated policies around telecom providers’ reporting of data breaches.

The disruption of Maryland’s reporting of COVID-19 data last month was caused by a ransomware attack, state officials said Wednesday.
Chip Stewart, the state’s chief information security officer, said the state has not paid extortion demands for the attack, which began on Dec. 4.
Impostazioni privacy
Questo sito utilizza i cookie per migliorare la tua esperienza di navigazione su questo sito.